We Secure Your Molecular Sims and Screens
Our drug discovery molecular simulation and molecular screening services are built on highly secure AWS and Oracle high-performance cloud infrastructures.
Set up a virtual coffee or contact us.
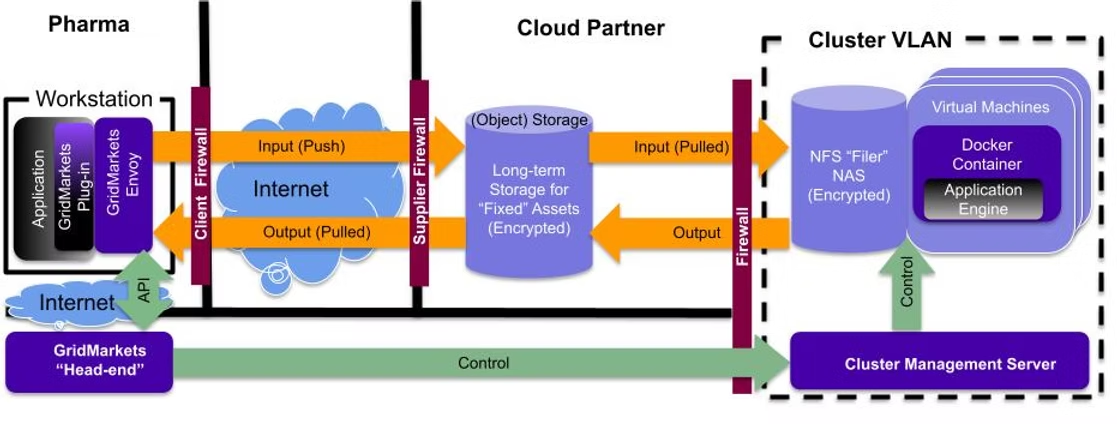
GridMarkets Security Architecture
GridMarkets Security Methods
NETWORK SECURITY:
No direct outside connections permitted.
MACHINE SECURITY:
I/O devices on all VMs are disabled.
AUTHENTICATION AUTHORIZATION:
GridMarkets has no access to our customer's environment.
LOGGING MONITORING:
Auto-scanning of logs for performance and security insights.
CONTENT MANAGEMENT:
Customer content is purged after 15 days of no access.
Network Security
- No direct outside connection to any of the VMs is permitted which greatly reduces the surface vector for any possible attack, simply by not exposing the compute nodes to the Internet.
- Network connections to/from VMs are controlled through a local NAT on every cluster.
- All traffic is strictly switched and confined to a designated cluster VLAN; no hubs or repeaters are used.
- Wireless communication is not used to transfer data within the GridMarkets infrastructure.
- All data transfers and API calls are via secure HTTPS connections (orange arrows).
Machine Security
- Input/Output devices on all VMs are disabled (e.g. to prevent any unauthorized USB devices).
- A VM instance is used only for one job & its files and is then destroyed, preventing any possibility of data being obtained by subsequent jobs by other users.
- All jobs run with normal user permissions with no access to administrative functions on the machine.
- Processing units are encapsulated in secure Docker containers within VMs to minimize security risks.
Authentication and Authorization
- GridMarkets has no direct access to clients’ environments through the applications and plugins it provides.
- These installed components only access information on GridMarkets’ systems via secure HTTPS connections for file listings or to transfer files.
- All access to GridMarkets’ servers is only via private keys with two-factor authentication that are not made available to anyone outside of GridMarkets.
- Authentication is over HTTPS to both the GridMarkets “Head-end” API (https://api.gridmarkets.com) and Job Manager Portal (https://portal.gridmarkets.com).
Logging and Monitoring
- Auto-scanning of logs for performance and security insights.
- Unexpected behavior can result in the shut-down of errant or all processes if deemed necessary.
- Suppliers of server capacity can only non-intrusively monitor behavior outside the VM, i.e. only analyze resource utilization and not its purpose.
Content Management and Transfer
- All data transfers are via GridMarkets’ purpose-built “Envoy” tool that uses industry-standard HTTPS for all transfers to & from Oracle's Cloud Storage where the data resides in individual account buckets and is authenticated using Oracle Service Accounts.
- Please see https://www.oracle.com/security/ for more information on Oracle's Cloud security.
- The client only needs access to this “Long-term Storage”; client firewalls only need to permit access to Oracle's domain via wildcard addressing.
- All content on suppliers’ servers is encrypted on disc with GridMarkets’ private keys (“Long Term Storage” & “Filer” above); user-specific private keys can be optionally used.
- Only the specific project (not even account) directory is NFS-mounted by the VMs, preventing access to any other location on the Filer.
- Content stored on suppliers’ servers is purged after a defined period of no access, or can be optionally deleted after transmission.
- Purpose-built, secured and dedicated VMs manage the transfer of content.